Managing the IT Asset Lifecycle for Sustainable SMB Growth
Managing the IT Asset Lifecycle for Sustainable SMB Growth
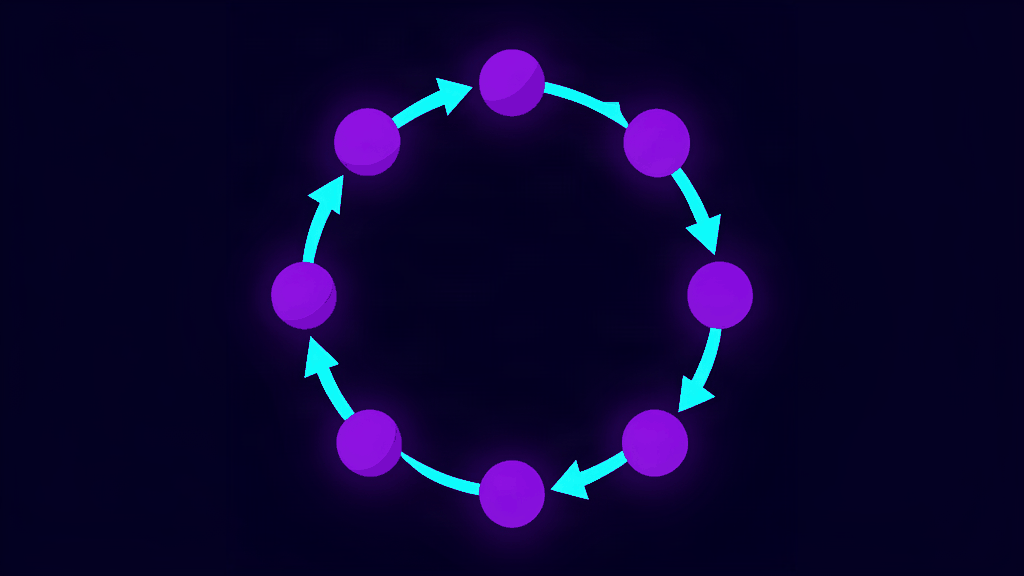
Maintaining visibility over every piece of hardware and software in a business is a constant challenge for growing companies. The it asset lifecycle provides a structured framework to manage these resources efficiently. IT asset lifecycle management is the systematic process of tracking and overseeing an IT asset from its initial procurement through to its final disposal. By treating technology as a lifecycle rather than a series of one-off purchases, businesses can reduce waste, improve security, and ensure employees have the tools they need to perform their jobs.
For most small to medium businesses, the challenge is a lack of formalized process. When a laptop is bought, it is often handed to an employee without being recorded in a central registry. When software is subscribed to, it may be forgotten until the renewal bill arrives. This fragmented approach creates blind spots that lead to overspending and security vulnerabilities. A disciplined lifecycle approach replaces this chaos with a predictable pipeline, allowing IT managers to shift from reactive firefighting to proactive planning.
Procurement and Planning: The Foundation of the Cycle
The lifecycle begins before a purchase order is signed. Effective planning involves identifying a genuine business need and determining the specifications required to meet it. Many organizations buy expensive hardware regardless of user requirements, leading to wasted capital and shortened useful life due to over-provisioning. A needs-based analysis ensures hardware is fit for purpose without being excessive.
Planning also requires an analysis of existing inventory. Before buying new equipment, IT managers should check if underutilized assets can be redeployed. This reduces unnecessary spending and prevents the accumulation of assets that sit in storage. Procurement should be centralized to ensure all assets meet company standards for compatibility and security. Decentralized procurement often results in a fragmented fleet, which complicates maintenance and increases the cost of spare parts.
During procurement, the concept of Total Cost of Ownership (TCO) is vital. The purchase price is only the first cost; the lifecycle includes power, cooling, software licensing, and deployment labor. A cheaper asset with a shorter lifespan often costs the business more over three years than a premium asset with a longer lifecycle. TCO analysis allows SMBs to make financial decisions based on long-term budget impact.
Every asset must be assigned a unique identifier upon procurement. Whether a serial number or a company-generated asset tag, this ID must be recorded in an asset management system immediately. This ensures the asset is tracked from the moment it enters the building, preventing loss and ensuring warranty information is available for future claims.
Deployment: Transitioning from Purchase to Production
Once procured, the deployment stage focuses on getting the tool to the user in a secure, configured state. Deployment is the process of establishing the operational baseline. For hardware, this includes installing the correct operating system, configuring security settings, and applying patches. Many organizations use a pre-configured software stack to ensure consistency and reduce manual setup time.
For software, deployment involves license allocation and access control. In an SMB environment, software asset management for SMBs is a practical necessity. Ensuring the right users have the right licenses prevents paying for unused seats and avoids legal risks. Deployment should always include a check against the current license pool to see if a seat can be reclaimed from a former employee.
A critical part of deployment is the assignment of ownership. Every asset must be linked to a specific user, department, or location. This accountability prevents assets from disappearing and allows IT teams to know exactly who to contact for security patches or hardware recalls. Without clear ownership records, deployment is merely a delivery, not a management process. This link is fundamental to the integrity of the entire lifecycle.
Deployment also provides a moment for initial user training. If a tool is deployed without orientation on security policies, the asset becomes a risk. Users must be informed of the acceptable use policy and the process for reporting failures. This reduces preventable hardware damage and ensures the asset remains productive for its maximum duration.
Usage and Maintenance: Maximizing Asset Value
The usage stage is the longest part of the it asset lifecycle. The goal is to maintain performance and security to extend useful life through proactive maintenance, routine updates, and periodic audits. Regular patching is the first line of defense, ensuring vulnerabilities are closed before they can be exploited. According to industry standards for IT asset management, the maintenance phase is where the majority of an asset’s value is realized or lost.
Maintenance includes monitoring the health of the asset. For hardware, this means tracking battery health or disk wear. For software, it means monitoring usage patterns to see if a tool has become shelfware. This is also where businesses encounter shadow IT, where employees install unapproved tools to solve immediate problems, bypassing the formal lifecycle and introducing risk.
To maintain accuracy, businesses must implement a regular audit cadence. You might wonder how often you should audit your IT assets to ensure the registry matches reality. Audits reveal discrepancies, such as assets moved without notification or software installed without approval. These checks ensure that data used for financial reporting and security planning remains reliable.
Ongoing maintenance also involves managing warranties and support contracts. A common failure in SMBs is allowing a warranty to expire unnoticed, leading to expensive repair costs. By tracking warranty dates in the registry, IT managers can decide whether to renew a support contract or move the asset into retirement. This prevents spending on aging assets that are no longer economically viable to repair.
End-of-Life and Retirement: Planning the Exit
An asset reaches end-of-life (EOL) when it can no longer support operational requirements due to hardware failure, the end of security updates, or obsolescence. Retirement is the process of removing the asset from production before it becomes a liability. As noted in the ServiceNow ITAM framework, retirement is a critical transition that prevents outdated technology from compromising network security.
The retirement phase requires clear criteria. If a laptop cannot run the latest security software, it should be flagged for retirement. Ignoring EOL markers is a common mistake in SMBs, where the belief that it still works justifies keeping outdated equipment. However, outdated hardware becomes a bottleneck for productivity and a gateway for attackers. Zombie assets are devices that are technically operational but no longer managed.
During retirement, the asset is decommissioned. This involves removing user access, uninstalling company software, and revoking licenses. The asset is then moved to a temporary holding area. Marking the asset as retired in the registry ensures it is no longer counted as an active resource during audits, preventing the company from paying insurance or maintenance costs for equipment that no longer provides value.
Retirement also provides a learning opportunity. By analyzing why an asset reached EOL, IT managers can identify patterns. If a specific brand consistently fails after three years, the company can adjust procurement standards to avoid that vendor. Retirement is the start of data collection for the next generation of procurement.
Disposal: The Final Step of the Cycle
The final stage of the it asset lifecycle is disposal. This is the most sensitive part because it involves the permanent removal of company data. Disposal is a legal and security requirement, involving the total destruction of data and environmentally responsible recycling. Incomplete disposal can lead to data breaches if a discarded drive is recovered by a third party.
Data sanitization is the absolute priority. Professional-grade wiping software or physical destruction ensures sensitive client data and intellectual property do not leave the company. Many businesses fail here by simply deleting files, which is insufficient to prevent recovery. Understanding what happens to old computers the right way is essential for maintaining compliance with laws like GDPR or POPIA.
After data is destroyed, the remains should be handled by a certified e-waste partner. This ensures toxic materials are not leaked and valuable metals are recovered. Professional partners provide a certificate of destruction, which is legal proof that the data was wiped and the hardware recycled. This certificate should be uploaded to the asset registry to provide a complete audit trail.
The process concludes when the asset is marked as disposed in the registry, closing the loop. For SMBs, this step is often neglected, leaving assets listed as retired indefinitely. Closing the loop is necessary for accurate financial accounting, allowing the company to write off the asset from the balance sheet.
Where IT Asset Lifecycle Management Breaks Down
Most organizations understand the theory, but execution fails due to a lack of integration. The biggest breakdown occurs when the asset registry is treated as a static spreadsheet rather than a living database. When procurement buys a device without notifying the registry manager, or when an employee leaves and their laptop remains assigned to them, the lifecycle is broken. This administrative friction leads to a decay of data quality.
Another failure point is the gap between retirement and disposal. Assets often sit in a storage closet for years. These forgotten devices are security risks because they contain old data and are not monitored. If a device is not disposed of promptly, it ceases to be a managed asset and becomes a liability. A successful process ensures a tight timeline between retirement and the final certificate of destruction.
Finally, many SMBs ignore software. While hardware is physical, software licenses are invisible. Businesses often overpay for SaaS subscriptions because they lack a process for retiring licenses when employees leave. This license leakage costs growing companies thousands of dollars per year. Applying the same rigor to software as to hardware finds significant cost savings and reduces the attack surface.
Frequently Asked Questions
What is the typical length of an IT asset lifecycle?
The length varies by asset type. Laptops typically have a lifecycle of three to five years, while servers and networking gear may last five to seven years. Software lifecycles depend on the vendor’s support window, but most enterprise applications require a review every twelve to twenty-four months to ensure they remain secure.
How does software differ from hardware in the asset lifecycle?
Hardware involves physical logistics, such as shipping and e-waste recycling. Software focuses on license entitlements, version control, and subscription management. While hardware wears out physically, software wears out when it becomes incompatible with new systems or is no longer supported by the developer, making it a security risk.
Why is an asset registry necessary for lifecycle management?
A registry is the single source of truth. Without it, there is no way to track an asset’s age, warranty status, or current user. It allows IT managers to predict when devices will need replacing, preventing unplanned capital expenditures that can disrupt a company’s cash flow.
What happens if an asset skips the retirement stage?
Skipping retirement usually means an asset moves directly to disposal or is simply forgotten. This leads to data leaks, as devices might be discarded without proper wiping, and financial inaccuracies, as the company pays for licenses for devices no longer in use.
How often should an organization review its lifecycle processes?
Lifecycle processes should be reviewed annually. As a business grows, its needs change. A process that worked for ten employees will fail for fifty. Annual reviews ensure procurement standards are current and the disposal pipeline meets legal and environmental requirements for the current scale of the business.
Conclusion
Implementing a formal it asset lifecycle transforms IT from a reactive cost center into a strategic advantage. By planning procurement, controlling deployment, maintaining usage, and securing disposal, businesses can ensure their technology supports growth rather than hindering it. The goal is total visibility, ensuring every asset is accounted for from the day it is ordered until the day it is recycled. This discipline reduces risk, lowers costs, and creates a sustainable foundation for operational success.